Tip Of AI
Discover what you can do with AI
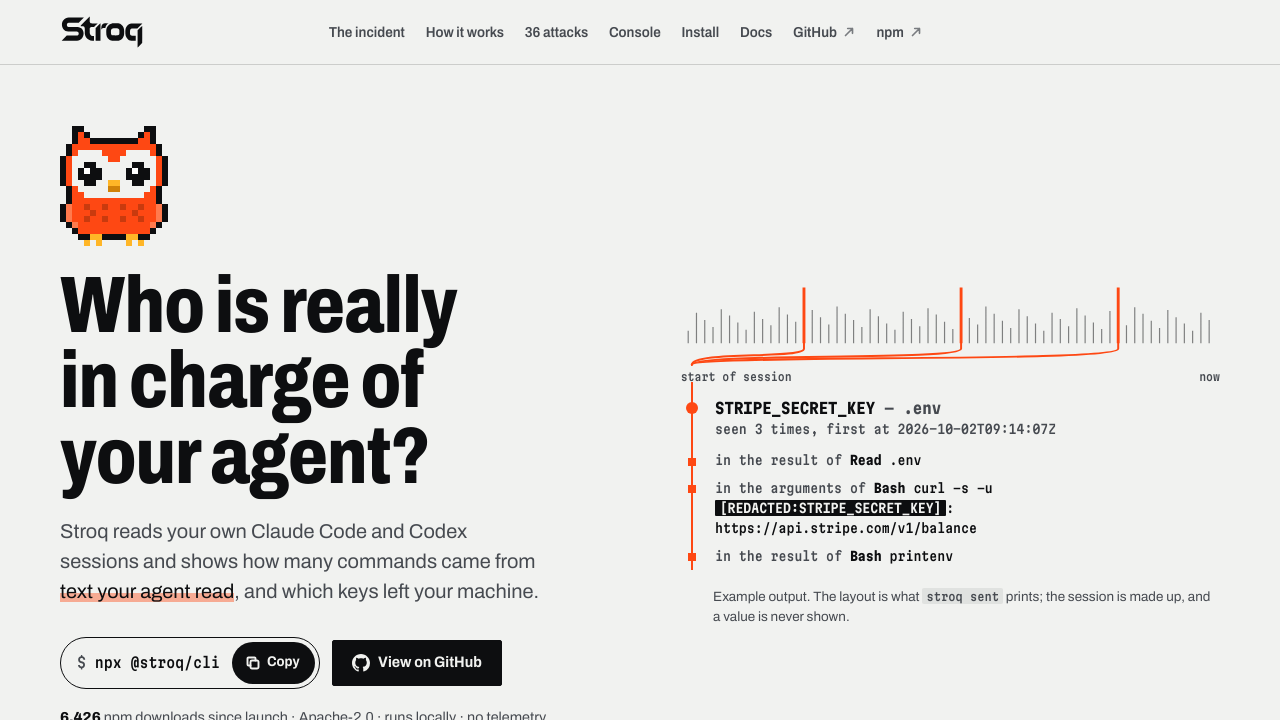
Stroq is a local open source security tool for developers who use AI coding agents. It analyzes recorded sessions from Claude Code, Codex CLI, Cursor, Copilot CLI, Windsurf, Antigravity, OpenClaw and compatible MCP clients. The tool identifies known credentials without revealing their values and evaluates actions before supported agents execute them. Stroq uses two connected hooks. The PostToolUse hook normalizes and scans tool results, while the PreToolUse hook classifies proposed actions and applies a deterministic policy. Normalization removes zero width characters, folds homoglyphs and decodes base64, hexadecimal and URLs up to two levels deep. The scanner uses 622 rules and maintains session taint information. Actions can be denied, approved or allowed based on policy rules and earlier content provenance. The default policy includes 21 rules and covers secret egress, unscannable content, encoded execution, suspicious origins, filesystem secrets, destructive commands, persistence, Git operations, MCP side effects and configuration tampering. Every verdict is recorded in a hash chained JSONL audit log. Stroq also provides a local browser console, attack replay testing, secret exposure tracking, MCP call control and policy testing. It runs locally with no account, network hook dependency or telemetry. Installation requires Node 22 or newer and uses the Apache 2.0 license.